Rsa Encryption: How It Works And Why It Issues
Multiplying two numbers, even very massive numbers, may be done quite rapidly on a pc. It is even surprisingly fast to tell if very large numbers are prime or composite (see AKS04 for this wonderful recent result in the long history of primality testing). Entro is the first platform to unify safety for AI agents, NHIs, and secrets and techniques —delivering full visibility, possession attribution, and real-time detection of anomalies.
Once the recipient has verified the padding, they know precisely where to find this message. It ensures that, when the concatenated string \(EB\) is converted to a big‐endian integer, the worth https://expandsuccess.org/developing-technical-skills-in-your-field/ is lower than the RSA modulus (that is, we don’t end up with a quantity too large for RSA to handle). You will better respect this fact once we dive into the arithmetic behind this. Alice sends a ciphertext to Bob after the initialization part.
The Euler Totient Operate
- These new algorithms goal to replace weak ones like RSA in crucial methods.
- This stability of visibility and safety makes RSA a reliable tool for digital certificates and past.
- However most fashionable RSA cryptosystems use the Carmichael function as a substitute of the Euler’s Totient Operate.
This handbook will assist you to understand the interior workings of the RSA algorithm, how they have evolved over time, and the schemes outlined beneath various RFCs. This knowledge will assist you to make knowledgeable choices about probably the most suitable RSA schemes depending on your small business requirements. Without it in place, attackers can reproduce keys generated under low entropy, leading to widespread vulnerabilities like the Debian OpenSSL bug of 2008, which uncovered thousands of SSL certificates. With correct primes and secure math, RSA protects your data with readability and confidence.
Implementation Of Rsa Algorithm
These points highlighted that a signature scheme have to be probabilistic to be safe in opposition to adaptive forgery makes an attempt and to make sure non-repudiation. This signifies that the signer should not be in a position to repudiate a signature because it’s bound to a random value known only at signing time. OAEP’s design makes such random legitimate ciphertexts astronomically unlikely (plaintext aware). Earlier Than https://britainrental.com/what-you-need-to-know-about-voice-tag-lab-the-main-benefits-of-the-program.html we begin, let’s get our symbols and abbreviations correct. We will use upper-case symbols (such as \(EB\)) to indicate octet strings and bit strings. We will use lower-case symbols (such as \(n\)) to indicate integers.

Characteristics Of Public Encryption Key
As a end result, you’ll be able to focus on higher-level features of your functions with out having to handle the low-level particulars of prime selection. The integer quantity n known as “modulus” and it defines the RSA key length. Using lengthy key sizes, proper padding, and safe RSA cryptography practices protects your information. For most use cases at present, RSA offers enough resistance to assaults. Attackers can monitor timing, power, or electromagnetic signals throughout encryption or decryption.
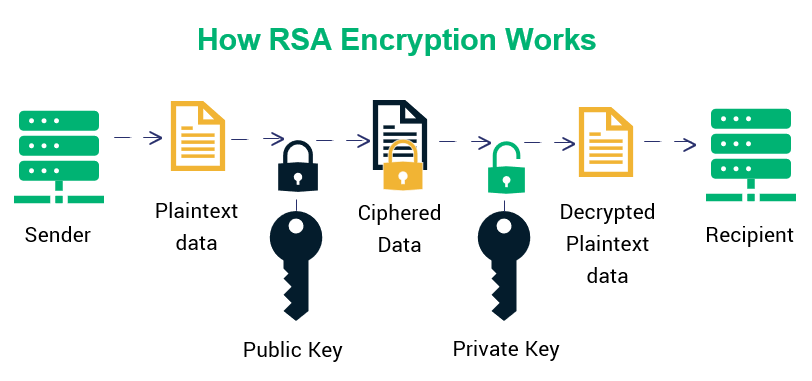
If someone makes use of keys shorter than the minimum key length or poor values for e and d, the whole system falls aside. Stick to greatest practices, 2048 bits minimal, with proper personal and public key pairing. That secret turns into a symmetric key used for the session, permitting easy knowledge trade. Because RSA offers a secure way to exchange keys with out prior communication, it lays the groundwork for encrypted connections and safe information transfer in every HTTPS session. The sender creates a symmetric key, encrypts it using the recipient’s public key, and transmits the encrypted key to the recipient.
We will choose SHA-1 as a hash perform in OAEP and \(hLen\) denotes the length in octets of the hash function output. We will later demonstrate why even MD5 or SHA-1 is a safe selection for OAEP even if it’s not collision resistant. Any RSA key the place \(d\) is bigger than \(λ(n)\) is considered non-compliant in those strict contexts. This successfully forces implementations to make use of the smaller \(λ(n)\)-based exponent, since any “oversized” \(d\) can be decreased \(mod ~~λ(n)\) to fulfill the criterion. To utterly appreciate this reality, let’s take a step back to grasp why the dimensions of the private exponent \(d\) issues in RSA. This can later be verified by others using the corresponding public key.
The scheme was proven plaintext-aware in the random oracle mannequin which implies that an adversary can’t concoct a legitimate ciphertext without understanding the corresponding plaintext. If an attacker tries to forge or tamper with ciphertexts, they virtually absolutely produce an invalid padding that might be rejected. The key takeaway from these attacks is that with out proper defenses. It is not immune to chosen-plaintext or chosen-cipher textual content assaults. This hole between the theoretical one-way perform (RSA’s trapdoor permutation) and a secure encryption scheme turned evident as implementers found that naive RSA could be “broken” by varied clever methods. A typical real-world example is a man-in-the-middle assault throughout a TLS handshake.